Remote Logging
Enrich and complement data collected by other SIEM systems with Cygna auditing records. Cygna Auditor enables you to configure integration with Microsoft Sentinel, Splunk, and any Syslog-compatible solution, and feed collected data to your audit streams in native format.
Configuring Remote Logging
To set up remote logging, navigate to Configuration / System / Remote Logging.
For Syslog:
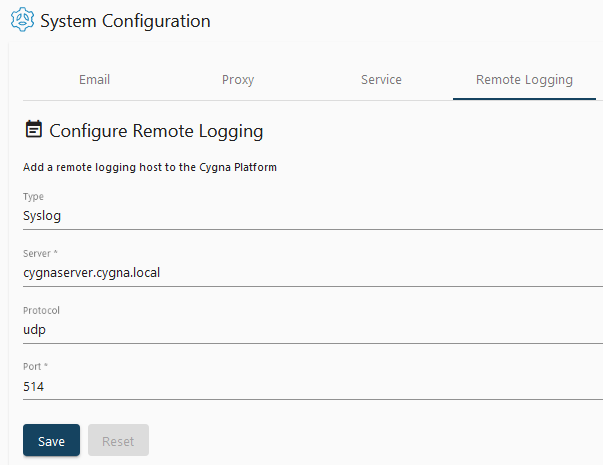
Specify the Syslog type, the remote server, as well as the port and protocol for connection.
When the protocol is set to TCP, you can secure the connection to the remote server:
- Use TLS—encrypts the connection to the Syslog server. This option is available for TCP only; it does not apply to UDP.
- Ignore certificate errors—accepts the server certificate even when it cannot be validated, for example when the server uses a self-signed certificate. This option appears only when Use TLS is enabled.
Note: If you switch the protocol to UDP, or turn off Use TLS, the TLS settings are cleared.
For Splunk:
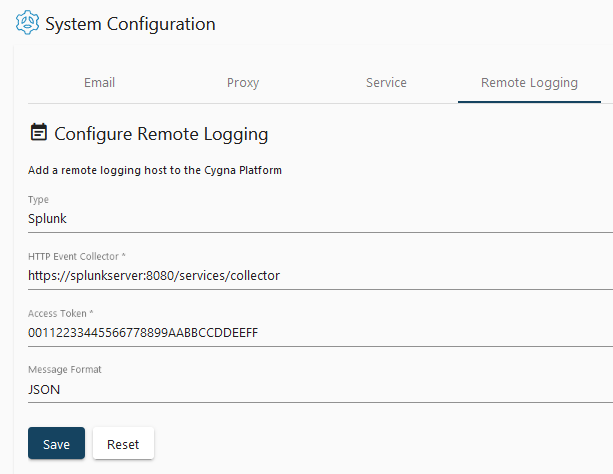
Specify the Splunk type, the Splunk URL, and access token. The data can be provided in JSON or rich text format.
For Microsoft Sentinel:
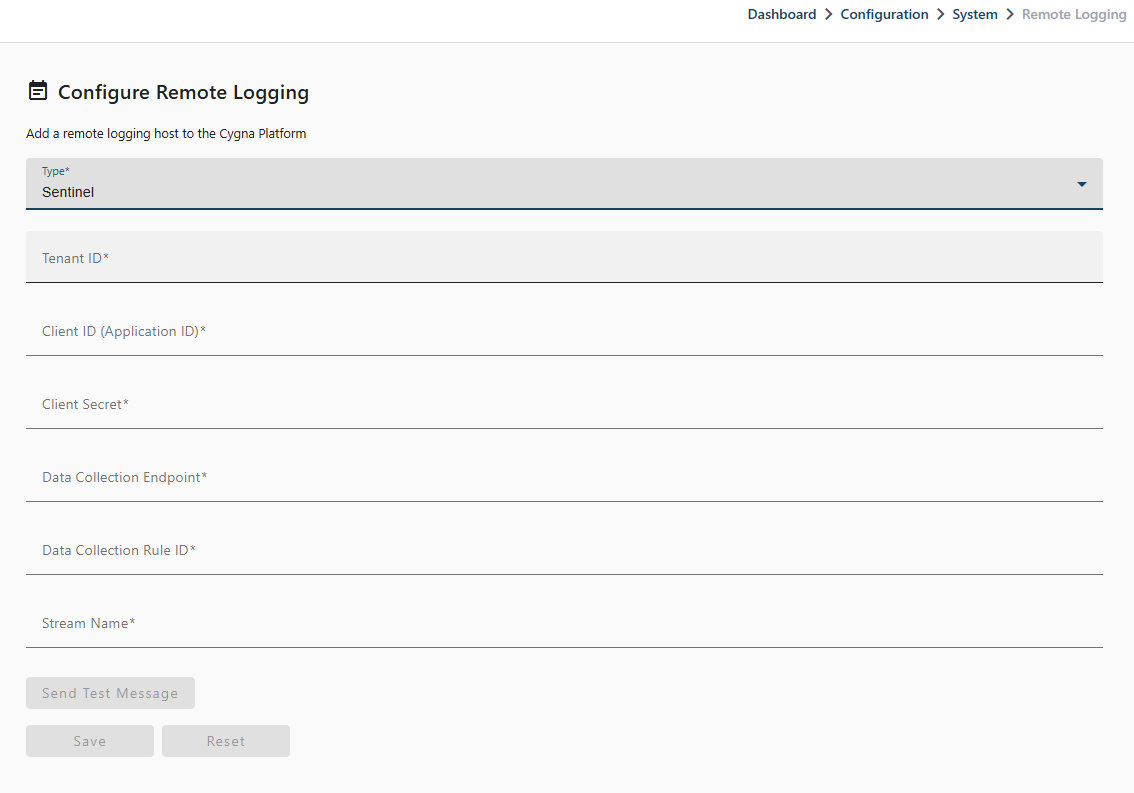
Cygna Auditor sends records to Microsoft Sentinel using the Azure Monitor Logs ingestion API. Before you configure the connection, prepare the following in Azure:
- An Entra ID application registration with a client secret. Grant the application permission to publish to the data collection rule.
- A data collection endpoint (DCE).
- A data collection rule (DCR), together with the custom table in your Log Analytics workspace that the rule writes to.
Specify the Sentinel type and complete the following fields:
- Tenant ID—the Entra ID tenant that contains the application registration.
- Client ID—the application (client) ID of the registered application.
- Client secret—the secret value generated for the application.
- Data collection endpoint—the URI of the DCE, for example
https://my-dce.westeurope.ingest.monitor.azure.com. - Data collection rule ID—the immutable ID of the DCR, for example
dcr-0123456789abcdef. - Stream name—the stream defined in the DCR, for example
Custom-CygnaAuditor_CL.
Verifying the Connection
For Syslog and Microsoft Sentinel, select Send Test Message to confirm that Cygna Auditor can reach the remote server before you save the configuration. The result is shown beside the button. This option is not available for Splunk.
Enabling Remote Logging for Reports
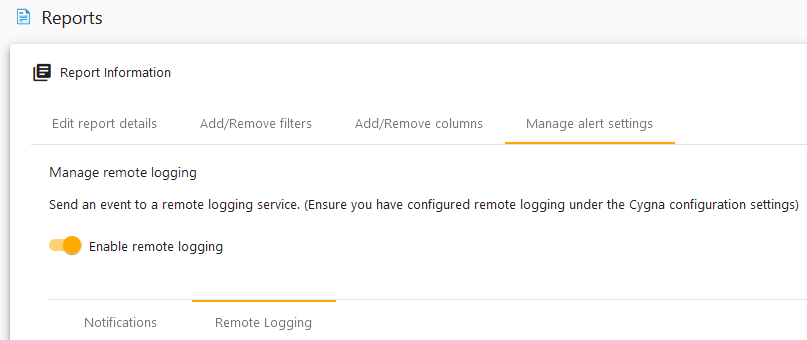
After you have specified the remote servers to feed data to, go to Reports and enable remote logging for each report you want to collect data for.
To do it, go to Reports, specify a report from the list, and then proceed to the Manage alert settings tab. Pick Remote logging and make sure to enable it. With this enabled, Cygna Auditor will send notifications to remote systems within two minutes of processing an event.