Configuring a Microsoft Subscription application
To collect audit events for Exchange Online, SharePoint Online, OneDrive, Entra ID Sign-ins, Entra ID, and Azure, make the following changes in your Entra ID tenant.
-
Log in to the Azure Portal. The account you use must be granted at least Cloud Application Administrator and Privileged Role Administrator roles.
-
Select Entra ID and then specify App registrations.
-
Select New registration to create a new Entra ID application.
-
Provide an application name (e.g., Cygna Auditor - Audit Events), specify the supported account types, and add a Redirect URI. Then select Register to create the new application.
-
Copy the Application ID and Directory (tenant) ID.
-
In the left navigation bar, select API permissions, select Microsoft Graph, and add the following permissions:
Permission
Type
AuditLog.Read.All
Application
Directory.Read.All
Application
Group.Read.All
Application
IdentityRiskEvent.Read.All
Application
Reports.Read.All
Application
User.Read.All
Application
-
Select Office 365 Management APIs, and add the following permissions:
Permission
Type
ActivityFeed.ReadDlp
Application
ServiceHealth.Read
Application
ActivityFeed.Read
Application
-
Select Windows Azure Active Directory, and add the following permissions:
Permission
Type
Directory.Read.All
Application
Member.Read.Hidden
Application
-
Select Grant admin consent to to confirm these permissions for the newly-created application.
- Navigate to Certificates & secrets and create a credential for the application. Cygna Auditor can authenticate using either a client secret or a certificate. For security purposes, use this credential only for auditing by Cygna Auditor.
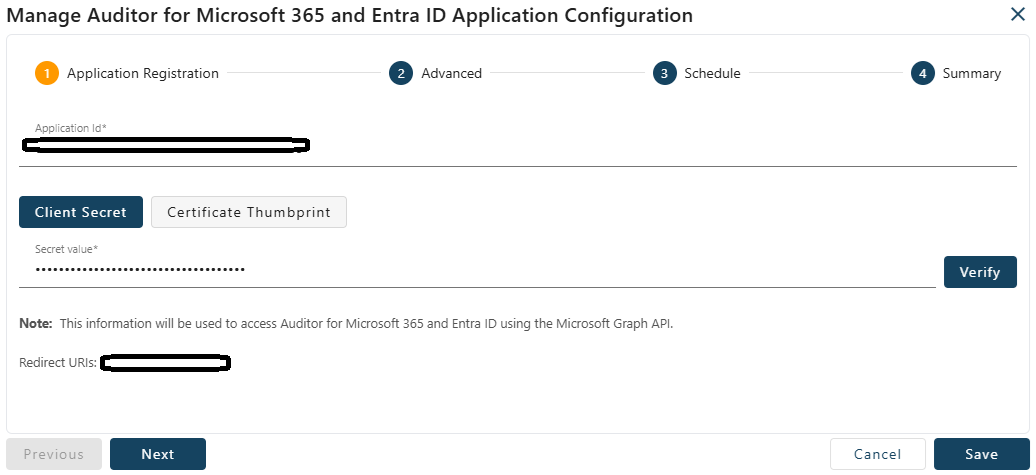
When you configure the collector in Cygna Auditor, select Client Secret or Certificate Thumbprint and enter the matching value:
To use a client secret:
Select New client secret, provide a description and expiry, then select Add. Note that recovery collections will stop after the expiry and you will need to generate a new secret at that time.
Copy the value to use later. These values will be inaccessible after you leave this screen.
To use a certificate:
Select Certificates, then upload the public key file (.cer, .pem, or .crt) of the certificate you want to use.
Copy the certificate Thumbprint to use later.
Install the certificate, including its private key, in the Local Computer\Personal certificate store on the server that hosts Cygna Auditor. The account that runs the Cygna services must have permission to read the private key.
Unlike a client secret, a certificate does not need to be replaced on a fixed expiry schedule set in Azure. Collections will stop when the certificate itself expires.